Hit by ransomware? We limit the damage right away.
Acting fast is crucial. We support you around the clock to stop the attack and secure your data.
To help you as quickly as possible, please have the following information ready:
- Symptoms: What did you observe?
- Time: When was the incident discovered?
- Scope: Which systems are affected?
- Actions: What steps have been taken so far?
Fast and professional help!
Ransomware often hits businesses without warning. The first few minutes decide whether the encryption can be stopped, the evidence secured, and operations restored. Hesitation risks letting the attack spread further through your network and affecting more data. We are there for you before an incident turns into a disaster.
aramido guides you through the entire incident, from the initial assessment and decision-making to full recovery. We coordinate the response with the ZAC, the German central contact point for cybercrime, secure evidence for insurers, and help you come out of the crisis stronger.
Immediate Intervention
You reach us directly with no waiting. We help you stop the spread and limit the damage.
Absolute Discretion
We work discreetly in the background, protect your reputation, and prepare the cooperation with law enforcement.
Forensic Excellence
We secure court-admissible evidence, reconstruct the attack path, and provide clarity for insurers, authorities, and internal review.
A structured approach to ransomware incidents
What is a ransomware attack?
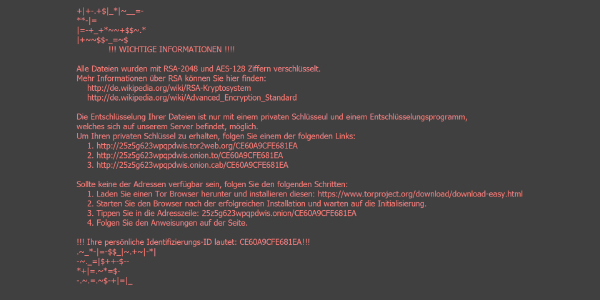
Ransomware is a type of malware that encrypts a company data and demands a ransom for its release. According to the Federal Situation Report on Cybercrime 2025 of the BKA, Germany alone recorded 1,041 reported ransomware attacks, an increase of ten percent over the previous year. Modern attackers copy data before encryption and threaten to publish it (double extortion), which often leads to a data breach. In the more advanced triple extortion, they also contact the affected business partners and customers to increase the pressure. aramido helps you handle the incident in a structured way, following the BSI and NIST standards, from the initial scoping to full recovery.
- 1Establishes an overview of which systems are affected and sets the priorities for the next steps.
- 2Affected systems are disconnected from the network and attacker communication is cut off. This keeps the incident contained.
- 3Memory, storage media, and network data are secured and analyzed. The goal is to reconstruct the entry path.
- 4We identify the initial entry vector of the ransomware and close it. Further vulnerabilities are addressed to prevent reinfection.
- 5Business processes are restored by priority, from backups or by rebuilding systems.
- 6The incident is reviewed and the cooperation with law enforcement is documented. This yields measures for the future.
Hit by ransomware? Request immediate assistance now!
Briefly describe what happened. Tell us which systems are affected, the time of the incident, and the amount of the demand. We help you limit the damage and develop your options. In urgent cases, reach us directly via our emergency hotline: +49 721 451 99 112.
What to do in a ransomware attack?
A ransomware attack throws a company into an exceptional situation. The first reaction often decides how things unfold. aramido supports you in every phase: we help isolate affected systems, secure evidence for prosecution, and assess whether recovery from backups is possible. For ransom demands, we provide a neutral analysis of the chances of success, the legal risks, and the practical alternatives.
Payments often fail to deliver the promised data recovery. According to Verizon's DBIR 2026 , the majority of those affected do not pay a ransom and restore their data from backups. aramido investigates the situation together with you and makes a recommendation on how to proceed. We also point out that paying ransom demands is not a sensible solution for good reason. We coordinate the incident with the ZAC and make sure your statutory reporting obligations under GDPR or NIS-2 are met.
Frequently asked questions about ransomware and incident response
Process incidents forensically, prevent future attacks
Digital forensics that hold up in court
The forensic analysis of a ransomware attack clarifies how the attackers gained access, which data was exfiltrated, and how long they were already moving through the network. We secure evidence to standards such as ISO/IEC 27037 and maintain an unbroken chain of custody. Our reports provide a basis for prosecution, insurers, and internal review.
Incident Response Readiness
How well prepared is your company for a ransomware attack? Incident Response Readiness means building processes and response capabilities before an attack demands them. This includes tested backup and recovery concepts, a crisis communication plan, and clearly defined decision paths. aramido analyzes your workflows together with you on site, identifies gaps, and closes them until your processes work reliably even under realistic pressure.
 Armin Harbrecht
 Andreas Sperber
 Kadir Ates
 Regina Okun